Microsoft Sentinel is the current name for the service previously called Azure Sentinel. It brings security information together so that suspicious activity can be detected, investigated and responded to from one place.
The important point for a business is not the product name. It is the ability to turn many separate security signals into something a trained person can understand and act on.
Why individual alerts are not enough
Microsoft 365, employee accounts, email and managed devices can all produce security alerts. Looked at separately, an alert may appear harmless or create unnecessary noise. When related activity is brought together, it can show a wider pattern.
For example, an unusual sign-in, a suspicious mailbox rule and activity on a company device may be connected. A combined view helps the person investigating understand whether the activity is legitimate or part of an attack.
What Microsoft Sentinel contributes
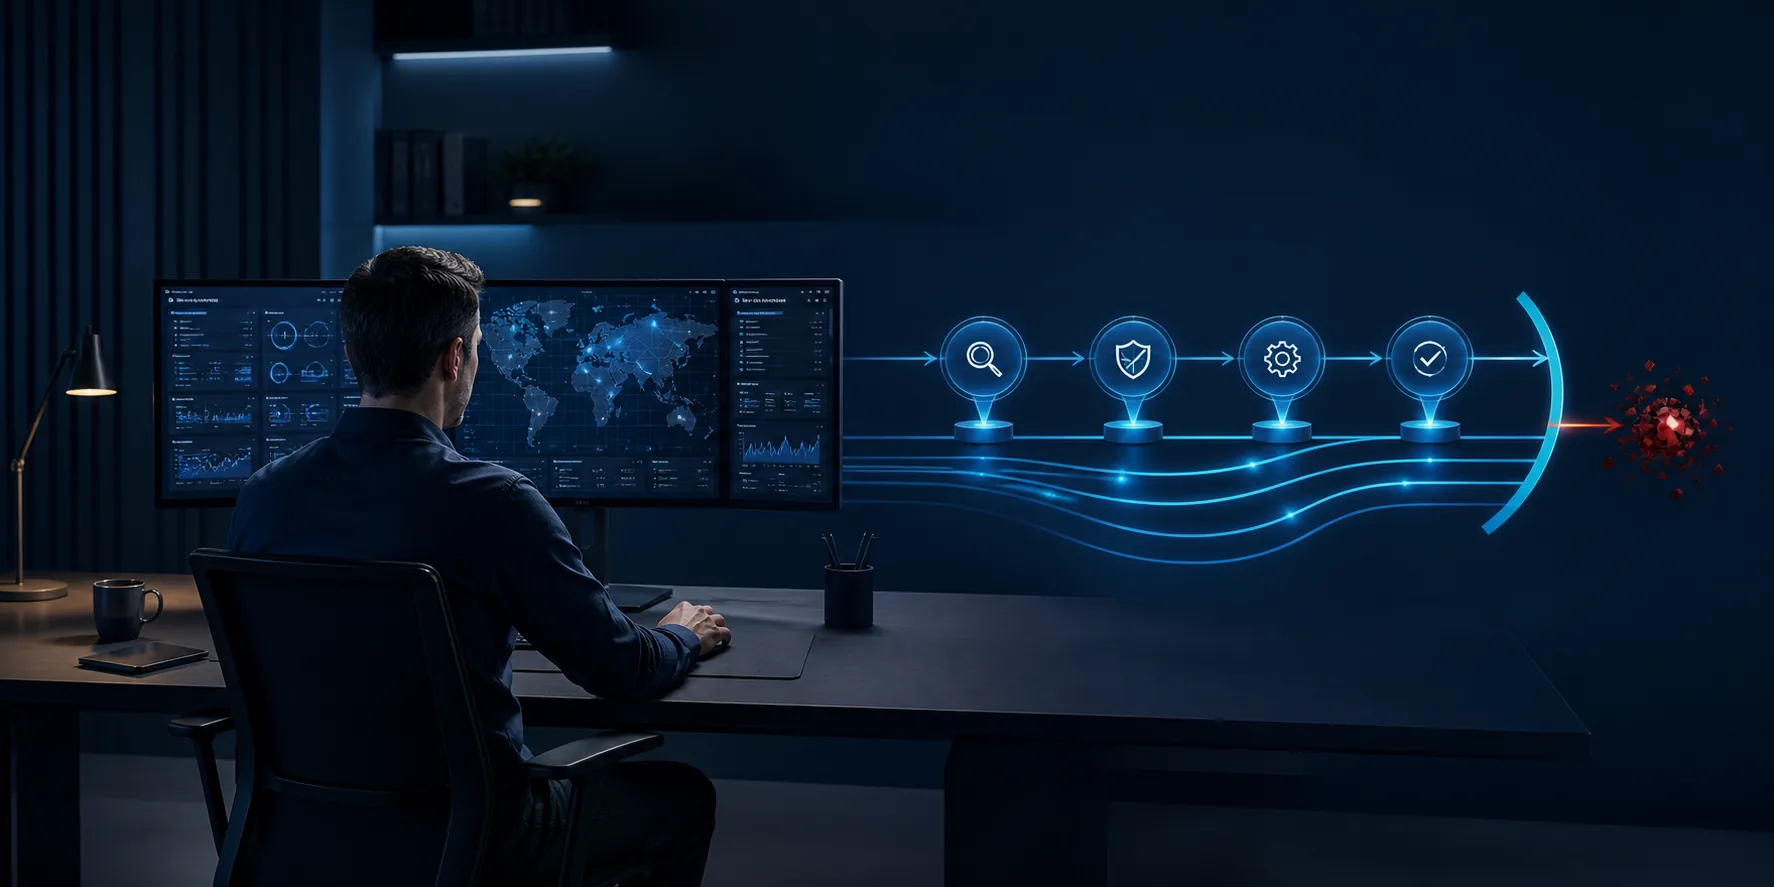
- Collection: relevant security information can be brought into one monitored service.
- Detection: rules and threat information help identify activity that deserves attention.
- Investigation: related alerts can be grouped so a specialist can see the sequence and likely scope.
- Response: agreed actions can be taken to contain genuine threats and protect the business.
- Reporting: activity and recommendations can be summarised for the people responsible for risk.
The human service around the technology matters
Collecting alerts does not provide protection by itself. Someone still needs to review the activity, rule out normal behaviour, investigate credible concerns and follow the agreed response.
That is why baseMSP presents this as 24/7 Microsoft 365 security monitoring, not as access to a dashboard. The client receives continuous monitoring, human investigation, response and a monthly report explaining what happened and what should be considered next.
Start with the right Microsoft 365 foundation
Continuous monitoring works best when accounts, devices and security controls are already managed consistently. The starting point normally includes suitable licensing, multi-factor authentication, controlled administrator access and an agreed security baseline.
A Microsoft 365 security review can establish that position before monitoring is introduced.
Further reading
Microsoft describes the current platform and its detection, investigation and response capabilities in the Microsoft Sentinel overview.